

SSH keys
Adding SSH public keys during installation lets you log in to your server as root without typing a password. This is more convenient and more secure than password-based login.
Adding keys during install
Section titled “Adding keys during install”SSH public keys are added through the Reinstall OS form. In the SSH Public Keys field, paste your public key or keys — one per line.
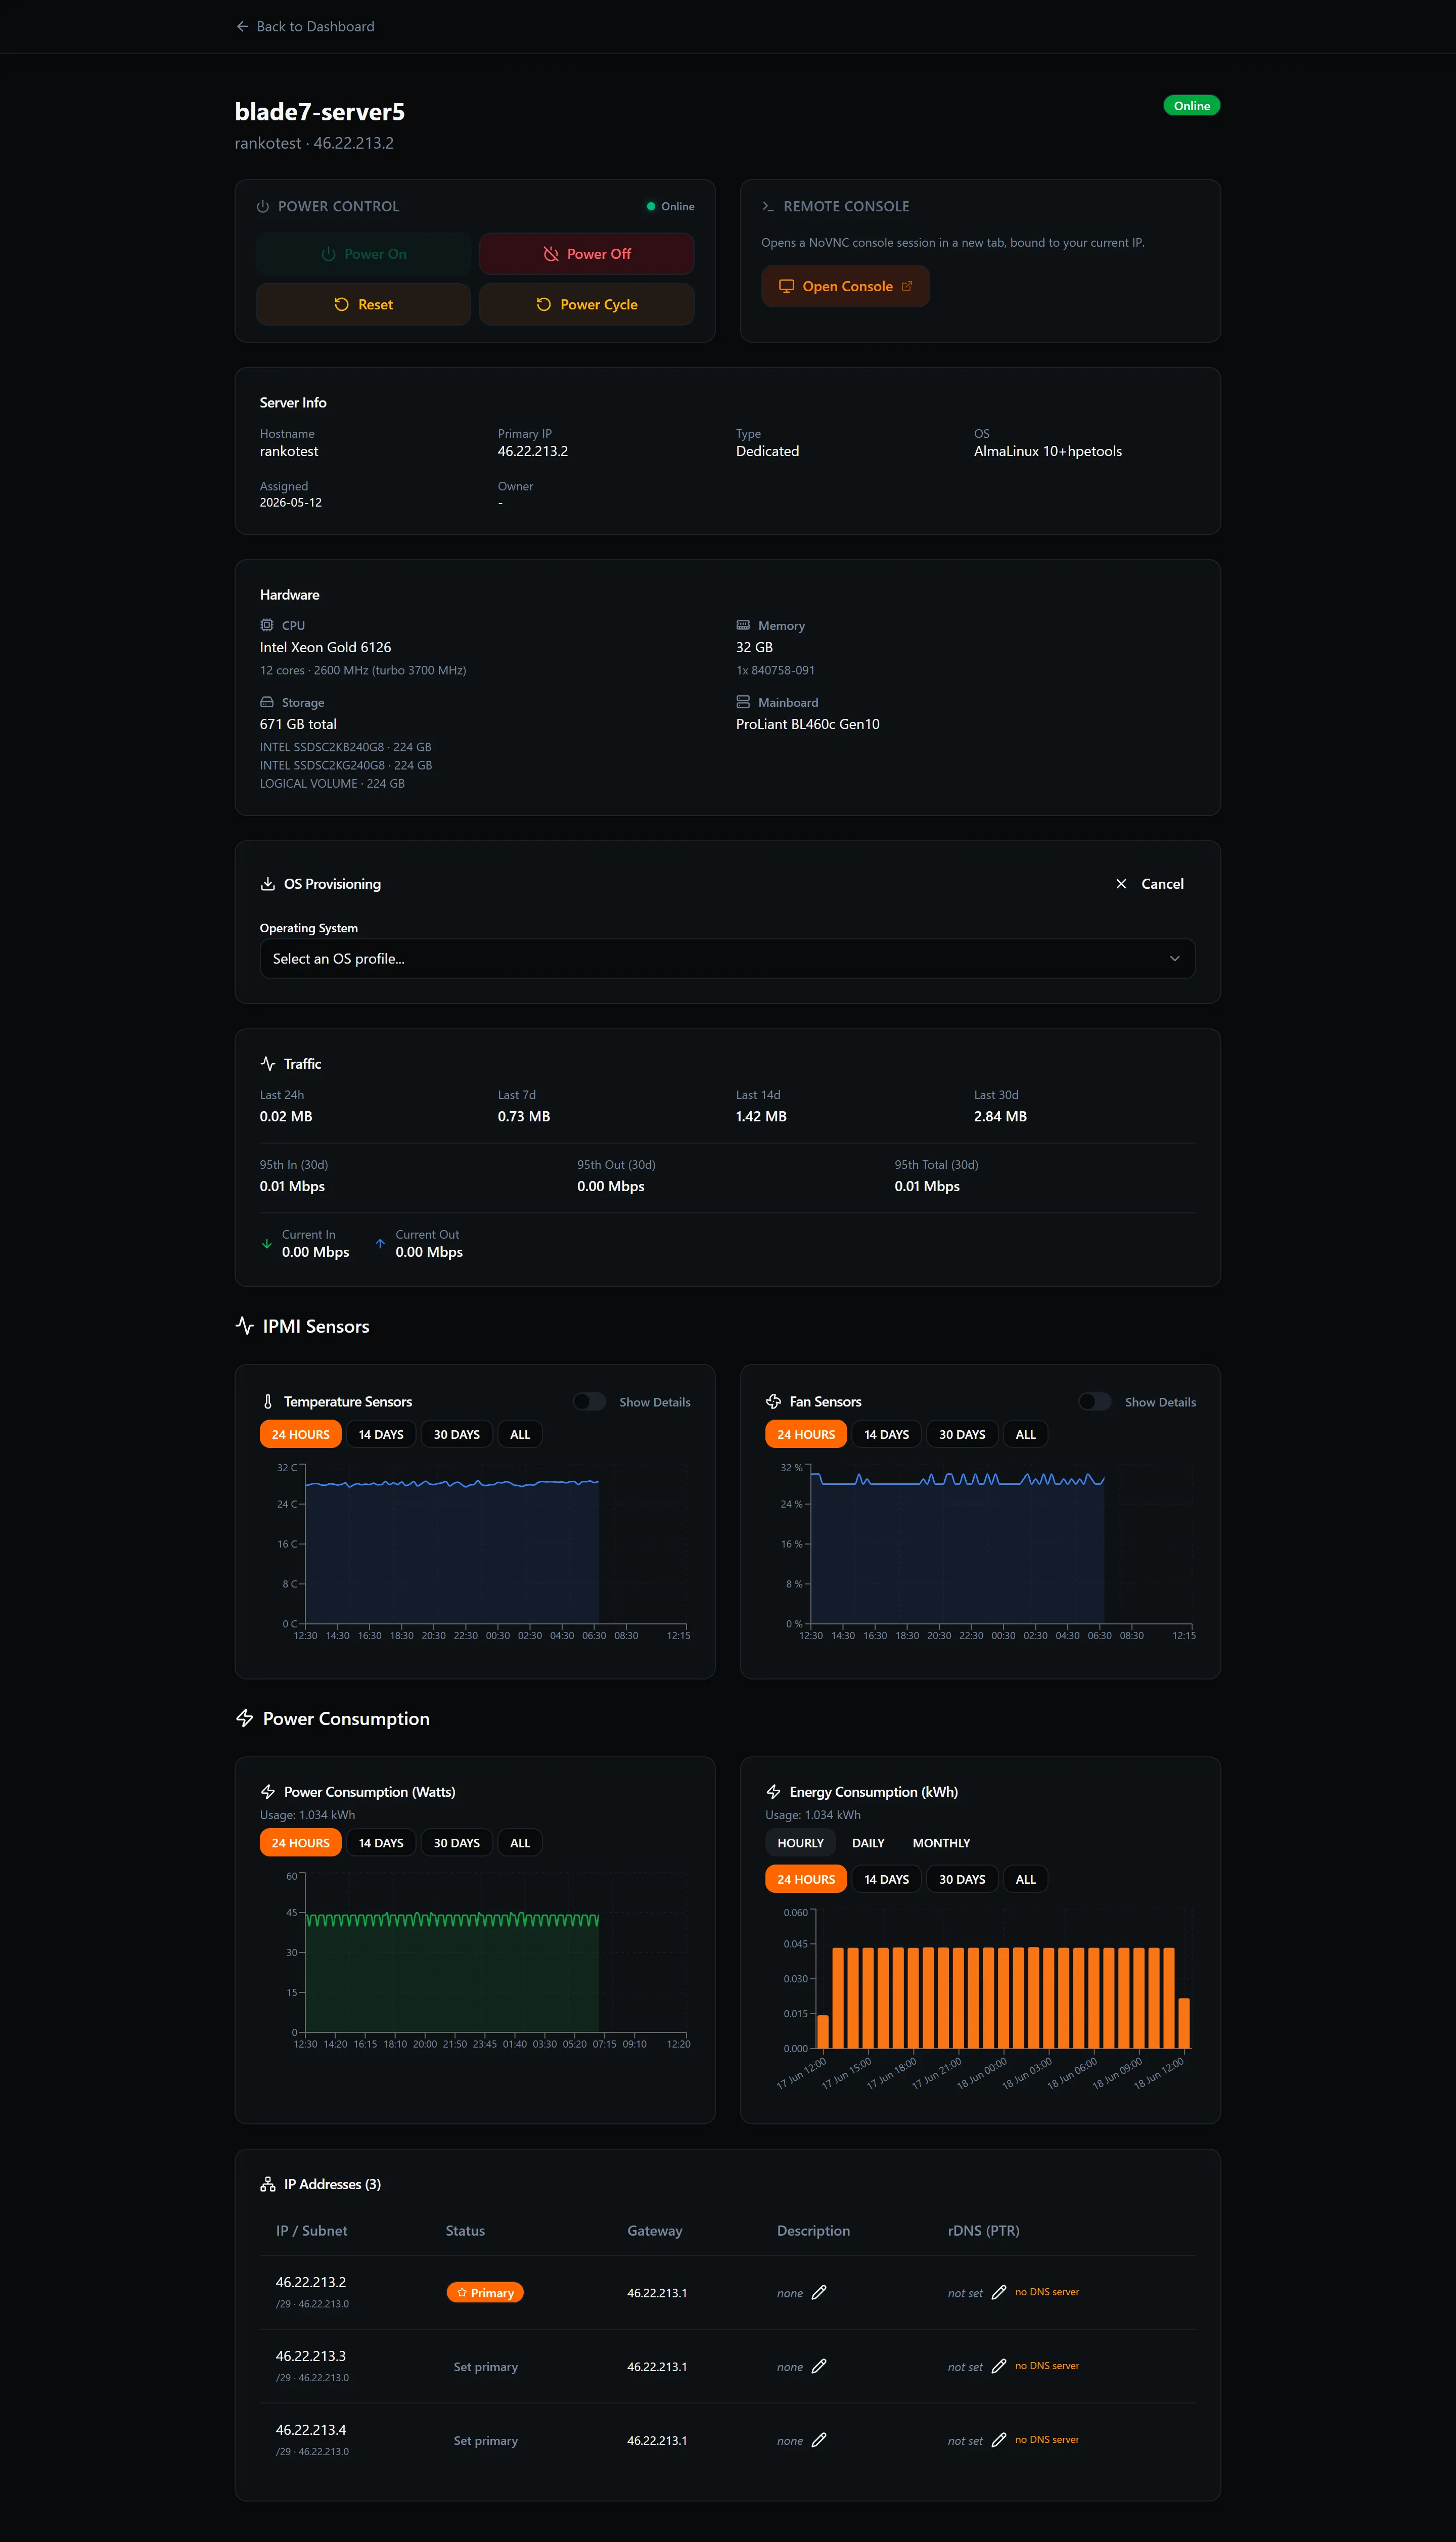
Keys are applied during installation and placed in /root/.ssh/authorized_keys. They take effect as soon as the server finishes installing and boots.
Key format
Section titled “Key format”Paste the full OpenSSH public key string. It looks like this:
ssh-ed25519 AAAA... you@hostCommon key types are ssh-ed25519 (recommended) and ssh-rsa. The key type comes first, followed by the base64-encoded key material, and optionally a comment (such as you@host) at the end.
If you have multiple keys — for example, one for each machine you work from — paste them one per line.
Generating a key pair
Section titled “Generating a key pair”If you don’t have an SSH key pair yet, generate one on your local machine:
ssh-keygen -t ed25519 -C "you@host"This creates two files: a private key (keep it secret) and a public key ending in .pub. Paste the contents of the .pub file into the SSH Public Keys field.
Keys are set at install time
Section titled “Keys are set at install time”SSH keys are written to the server only during an OS installation. To add or remove a key on a running server, edit /root/.ssh/authorized_keys directly via SSH or the console.